Call Mr. Robot: Malware Attack Targets Android Users' Banking Apps
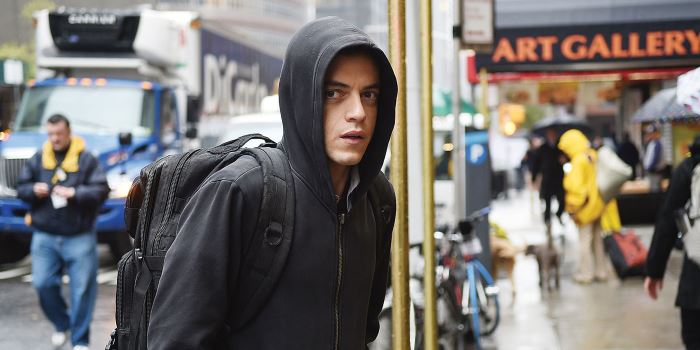
Australia’s big four banking apps have been targeted by a sneaky Android malware attack.
According to the Sydney Morning Herald, the apps for Commonwealth Bank, Westpac, National Australia Bank and ANZ Bank are all at risk of being compromised by the malware, which hides on infected devices and waits until users open those apps up to strike. The malware then tries to fool users by popping up a fake login screen and capturing usernames and passwords. It’s not just the big four being targeted by hackers either. Apps for Bendigo Bank, St. George Bank, Bankwest, ME Bank, ASB Bank, Bank of New Zealand, Kiwibank, Wells Fargo and several Turkish banks, not to mention PayPal, eBay, Skype, WhatsApp and several Google services are also seeing their login screens mimicked by the malware. As if this wasn’t all terrifyingly invasive enough, the malware is able to intercept two-factor authentication codes (for instance, when you also get the app to SMS a code that allows you to finalise your login). The malware forwards the code to hackers without the user ever realising. So, here’s what you need to look out for, Android users: The malware finagles its way onto your device by pretending to be the Adobe Flash Player application. It will ask to be installed, and then, once installed, request device administrator rights. That’s when it looks for your installed banking applications and begins downloading the fake login screens. The good news is that Android devices have a default security option to keep you from downloading apps from unknown sources. You would have to override that option and download the app (from outside of the official Google Play app store) to become vulnerable to the malware sneak attack. Keep an eye on any downloads coming from flashplayeerupdate.com, adobeflashplaayer.com and adobeplayerdownload.com. These are the danger zones. If you’re worried you’re already infected, go to Settings > Security > Device Administrators and see if ‘Flash Player’ is listed there. If you attempt to remove it, don’t panic when it says “data may be lost”, as it’s just trying to trick you. (So tricky, this malware!) Uninstall that sucker. If it keeps fighting your deactivation, restart your device in Safe Mode, which will allow you to uninstall it without interruption. Here’s some inspiration for your battle with the malware.Photo: USA.
Comments & Feedback
Share your opinion
Emoji cheatsheet Formatting Comment guidelines